Enroll endpoints without a walk-through
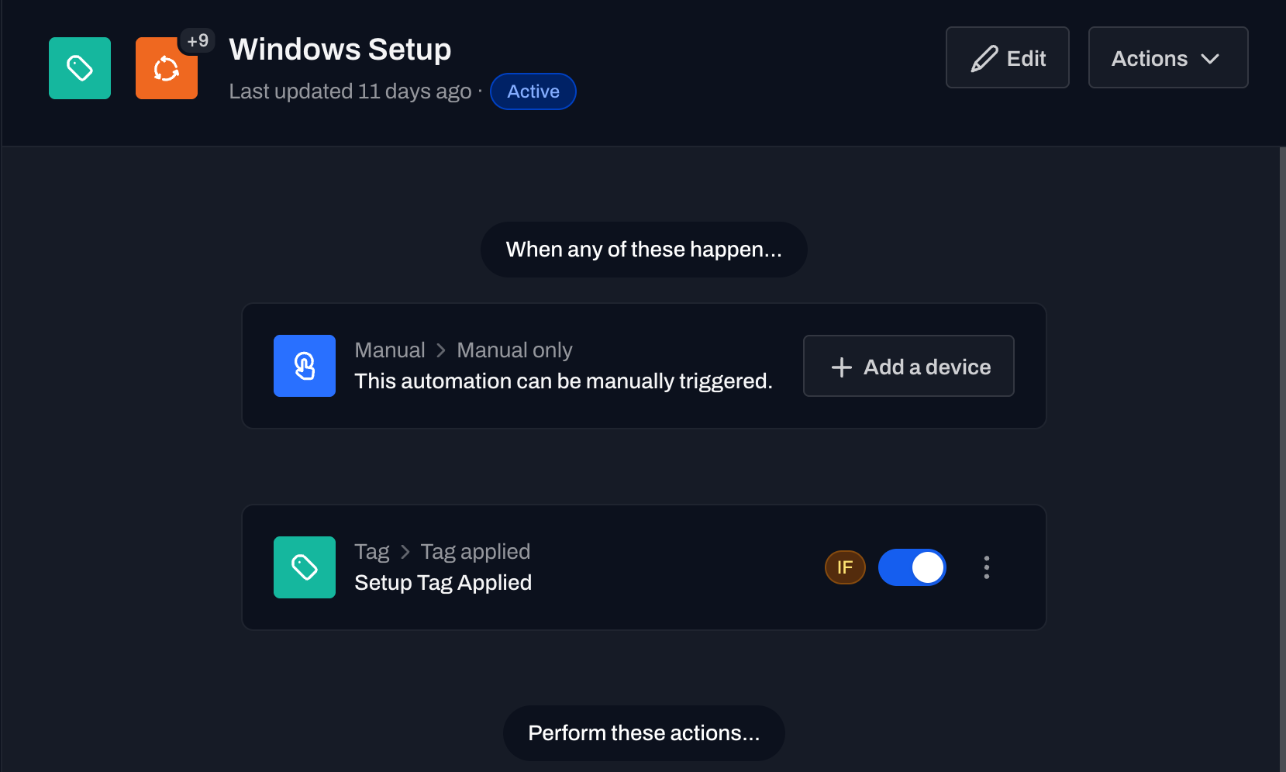
A new workstation is detected, approved, and configured by the same Device Management automation. Clinic and nurse-station devices join the fleet without a desk visit.
SOC 2 Type II examined, encrypted end to end, and logged down to every action.
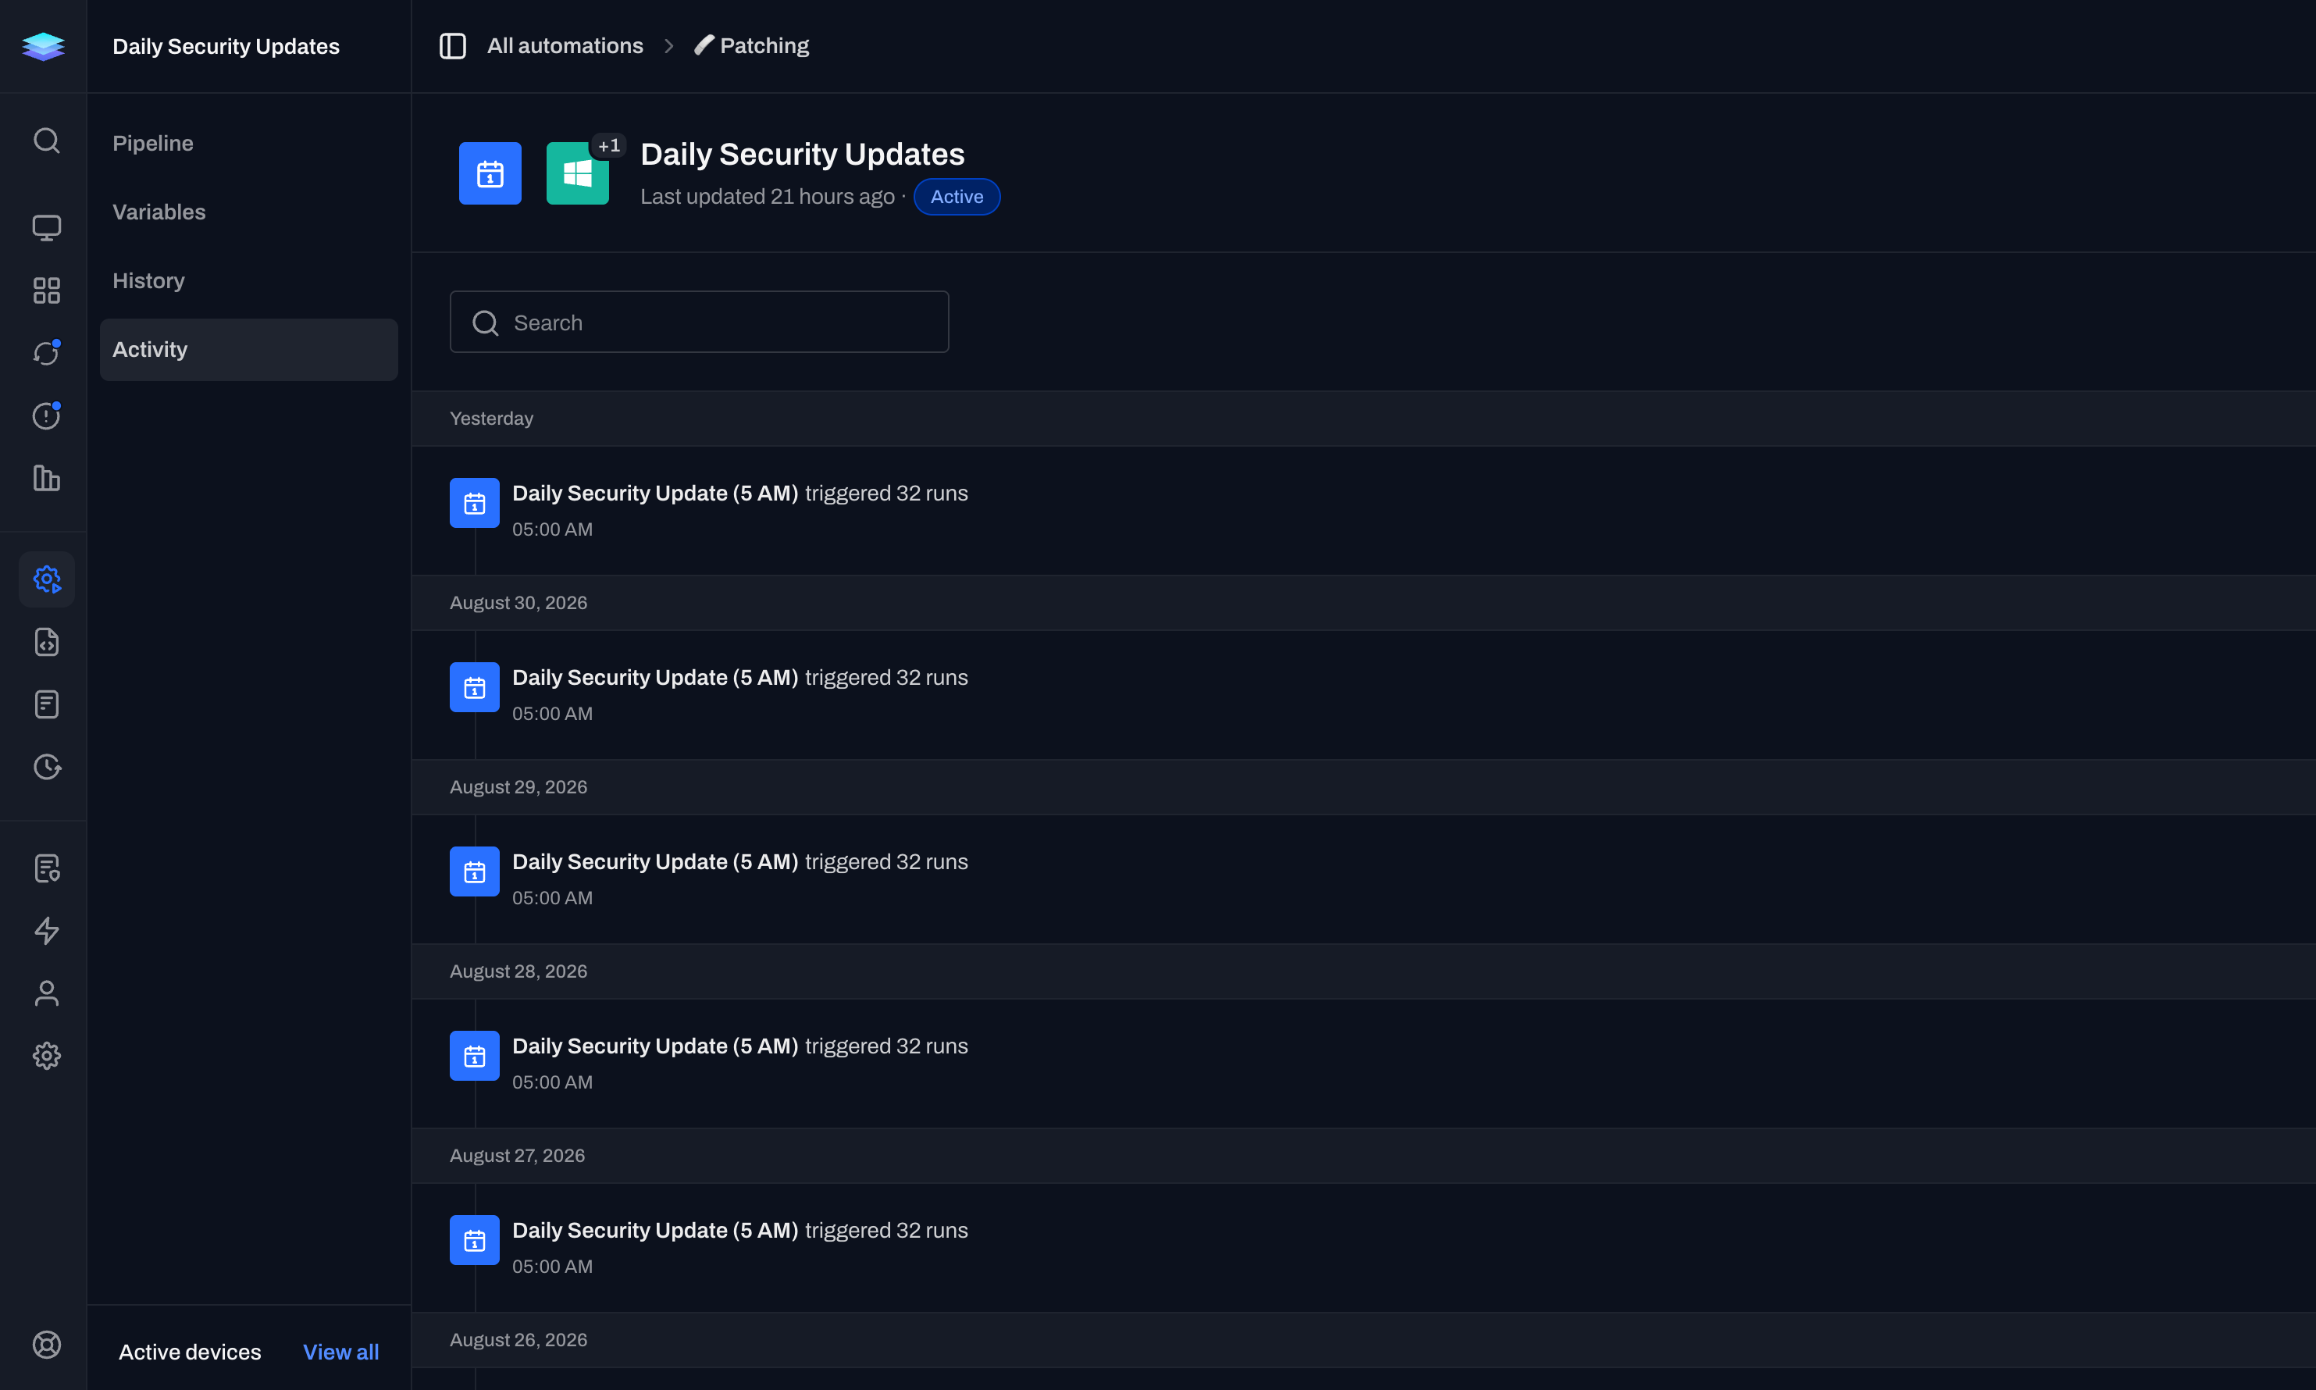
Keep updates out of a shift.
A missed patch is a vulnerability. An unsecured session is an audit finding.
When a clinical endpoint goes down, patient care waits with it, so it is never just an IT ticket.
Unpatched endpoints are real risk, yet reboots and disruption are not an option in the middle of a shift.
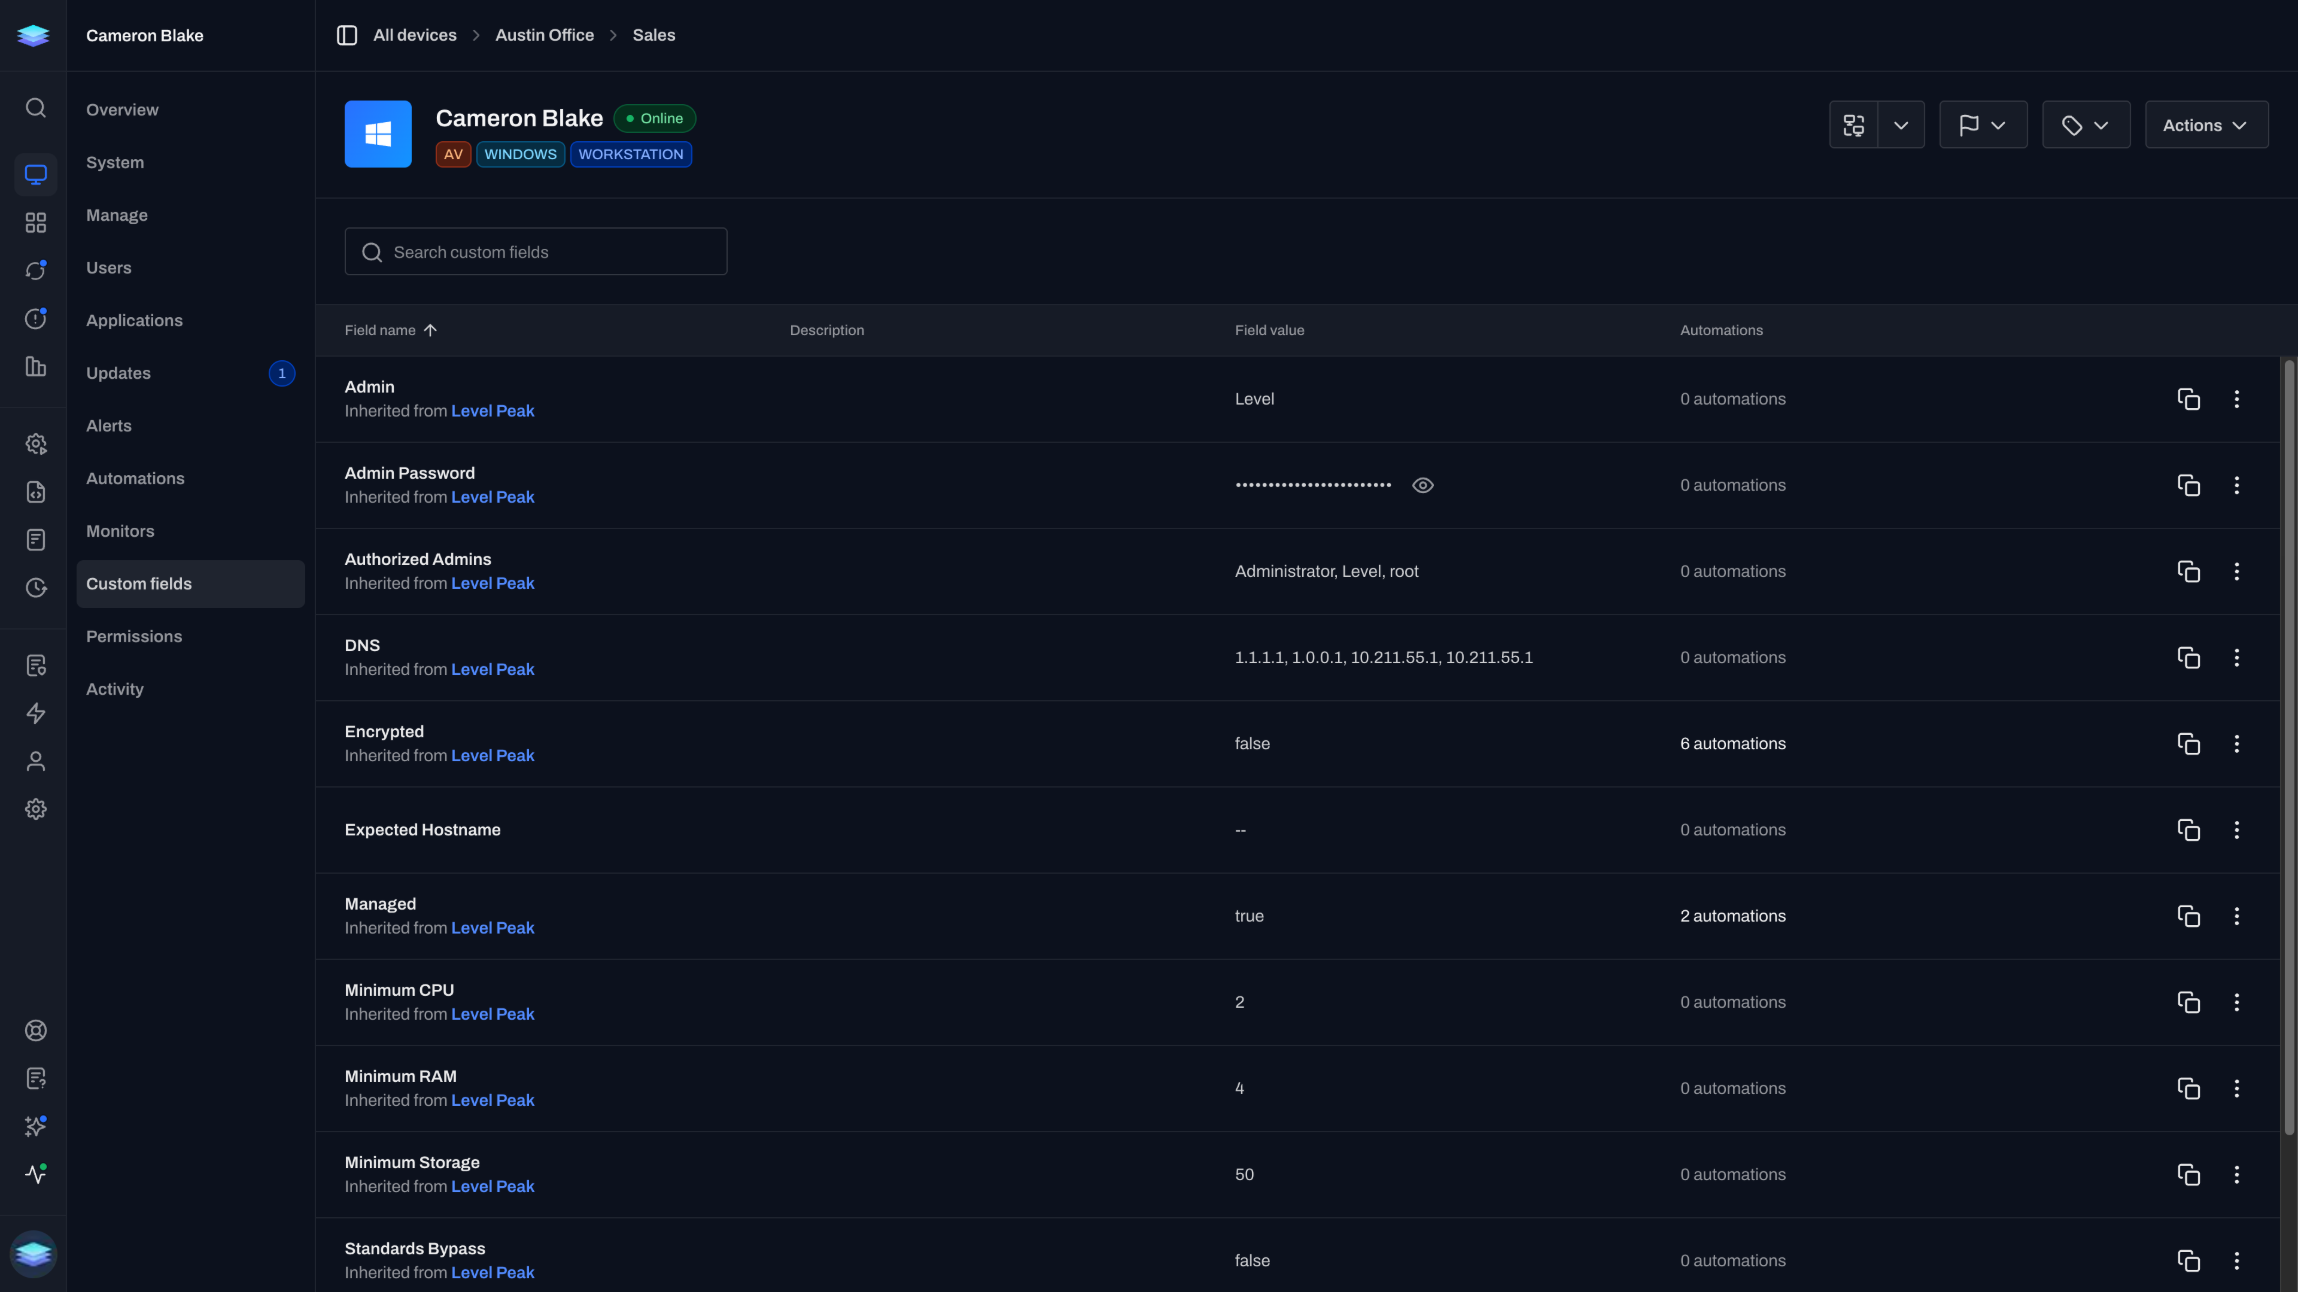
PHI lives on devices across clinics, nurse stations, and admin desks, so access and audit cannot be afterthoughts.
The tool should match them.
Open the page for the job in front of you.
The onboarding pipeline starts the moment they appear.
A new workstation is detected, approved, and configured by the same Device Management automation. Clinic and nurse-station devices join the fleet without a desk visit.
Sourced reviews on remote access, Linux, and real-time ops.
“Level’s in-browser remote access is very good. If you need interactive remote access without a helper app, Level is a much better choice.”
“Level boasts top-notch automation and scripting capabilities, handles patch management efficiently, provides robust remote management tools, and most importantly, it is regularly updated with new features.”
“What they do well is the automation module, monitoring, and scripting. Everything works in real time, without delay.”
“Our patching routines are more successful than they have been with past products. We have been especially pleased that Level has continuously improved the product.”
“I personally use Level.io internally here at NovaBACKUP to monitor production endpoints around the world. It works very well, saves us a ton of time with automations, monitoring, and alerts, and the company has been very responsive for any support issues or feature requests.”
“Level gives us the power for only a few technicians to manage hundreds of endpoints from anywhere in the world with real-time insight.”
“Like others have said, our team is also really enjoying Level. It’s very refreshing to have a super modern and sleek interface, great Linux support, and a development team that actually listens to feedback. It’s also really exciting to see the new features roll out basically every month.”
“Level has brought us the multi-OS management software we need at a reasonable price. Its modern UI makes it easy to work with systems individually and in bulk.”
Know the moment a clinical endpoint fails.
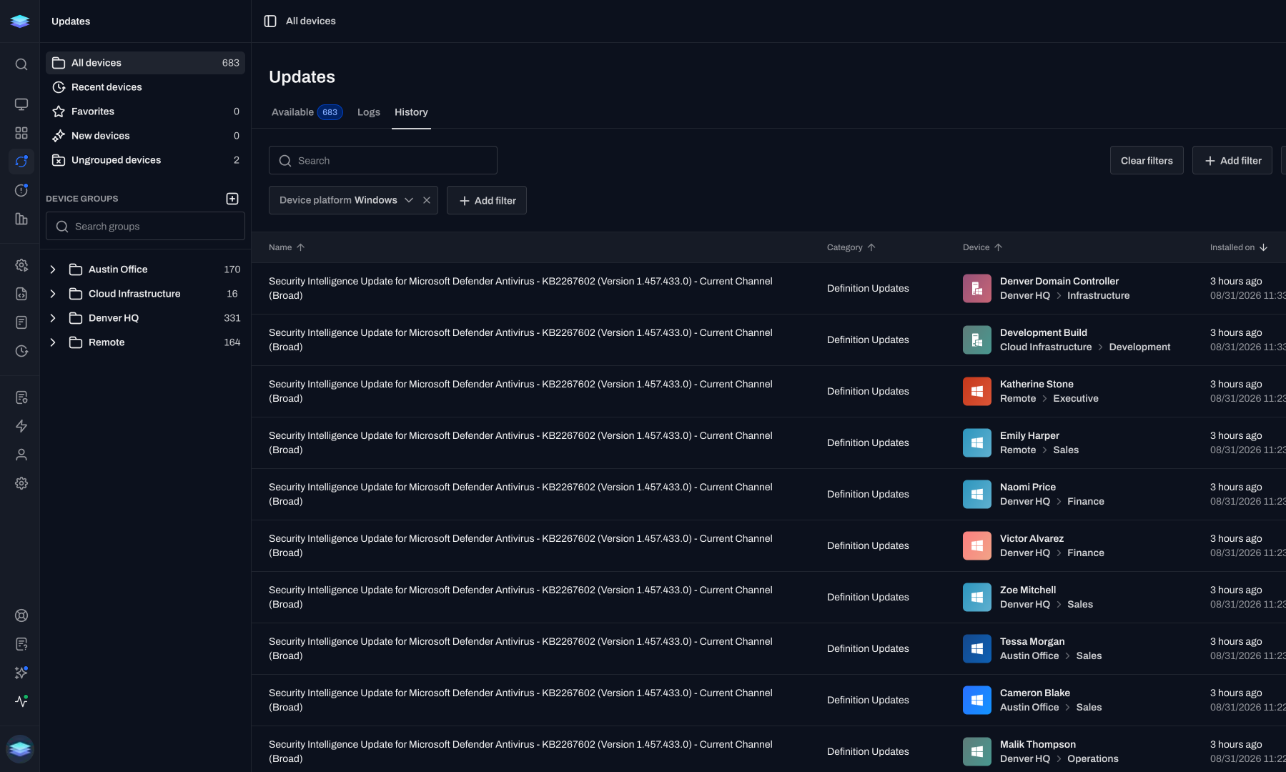
Watch patch and workflow progress on clinic and nurse-station devices without waiting for the next scan.
Certifications, encryption, audit logs, and patch control.
Yes. Level maintains a SOC 2 Type II report covering controls that include role-based access, audit logging, and encrypted remote sessions.
Remote sessions are encrypted end to end. Level uses a P2P connection when network conditions allow and an end-to-end encrypted relay when they do not. Our security team can walk through the exact in-transit and at-rest architecture during a review.
Sessions, script runs, automation runs, and patch events are recorded with the user, device, timestamp, and action, so you can show what happened and who did it.
Level helps you standardize, document, and enforce the endpoint controls that support HIPAA-aligned operations. Compliance belongs to the organization, not to any single tool.
Yes. A Business Associate Agreement is available on request via support@level.io (separate versions for internal IT and MSPs).
Yes. Schedule patches in approved windows, scope them by device group, and track completion from the Updates page so updates never collide with care.
Windows, macOS, and Linux through a single agent, across clinical and administrative endpoints alike.
Book a 1-hour demo and we'll walk through the encryption, access controls, and audit trail on a live environment.